Top 25 Website Security Misconfigurations (2026)
Security misconfigurations remain the #1 most exploited vulnerability class — not because developers don't care, but because modern web stacks are layered, complex, and constantly changing. In 2026, the attack surface has expanded to include AI APIs, cloud-native services, and edge computing — making even a single misconfiguration catastrophic.
This guide covers the 25 most dangerous and commonly found website security misconfigurations observed in real-world VAPT (Vulnerability Assessment and Penetration Testing) engagements, bug bounty reports, and incident response cases in 2025–2026.
What Is a Security Misconfiguration?
A security misconfiguration occurs when a system, application, or service is set up incorrectly — exposing it to attackers. Unlike vulnerabilities in code logic, misconfigurations are often introduced during deployment, upgrades, or by leaving default settings untouched.
They are insidious because:
- They're often invisible to developers who focus on features.
- They can bypass sophisticated code-level security controls.
- They frequently survive code audits because they live outside the codebase.
Per OWASP Top 10 (2021), Security Misconfiguration ranks #5 — but in real-world VAPT engagements, it's consistently the most frequently found category.
The Top 25 Misconfigurations
🔴 CRITICAL
1. Default Credentials Left Unchanged
What it is: Admin panels, databases, IoT devices, and cloud dashboards shipped with well-known default credentials (e.g., admin:admin, root:root, admin:password).
Real-World Impact: In 2025, a major SaaS platform was breached because their staging PostgreSQL instance used the default postgres:postgres credentials exposed on a public subnet.
Fix:
- Enforce credential change on first deployment.
- Use secrets management tools (HashiCorp Vault, AWS Secrets Manager).
- Scan infrastructure with tools like Nuclei or Shodan probes.
2. Exposed .env and Configuration Files
What it is: Files like .env, config.json, database.yml, appsettings.json, or .aws/credentials are accidentally committed to version control or left accessible via the web root.
Example: https://example.com/.env returning:
DB_PASSWORD=supersecret123
AWS_SECRET_ACCESS_KEY=AKIAIOSFODNN7EXAMPLE
Fix:
- Add
.env,*.pem,*.key,*.secretto.gitignore. - Use
git-secretsortruffleHogin CI/CD pipelines. - Deny access to dotfiles in your web server config.
# Nginx — block dotfiles
location ~ /\. {
    deny all;
}
3. Directory Listing Enabled
What it is: Web servers with directory listing enabled allow attackers to browse the file system, discovering backup files, source code, logs, and sensitive data.
Fix:
# Nginx
autoindex off;
# Apache
Options -Indexes
4. Verbose Error Messages in Production
What it is: Stack traces, database error messages, framework version info, or internal file paths returned to the end user — a goldmine for attackers during reconnaissance.
Example:
RuntimeError at /api/users
psycopg2.errors.UndefinedTable: relation "user_sessions" does not exist
LINE 1: SELECT * FROM user_sessions WHERE...
/app/api/views.py, line 142
Fix:
- Set
DEBUG=Falsein production. - Use generic error pages (HTTP 500, 404).
- Log detailed errors server-side only.
5. Missing or Misconfigured Authentication on Admin Endpoints
What it is: Administrative endpoints (/admin, /manage, /actuator, /debug) left unauthenticated or protected by only IP-based restrictions that can be bypassed via X-Forwarded-For headers.
Fix:
- Require strong authentication + MFA for all admin routes.
- Never rely solely on IP-based access controls.
- Implement network-level firewall rules in addition to application-level auth.
6. Spring Boot Actuator Exposed (Java/Kotlin)
What it is: Spring Boot's /actuator endpoint, when exposed without auth, leaks environment variables, heap dumps, active beans, thread dumps, and more — often including credentials.
Exposed Paths:
/actuator/env
/actuator/heapdump
/actuator/mappings
/actuator/shutdown  ← can kill the app
Fix:
# application.yml
management:
  endpoints:
    web:
      exposure:
        include: health, info  # Only expose what's needed
  endpoint:
    health:
      show-details: never
🟠 HIGH
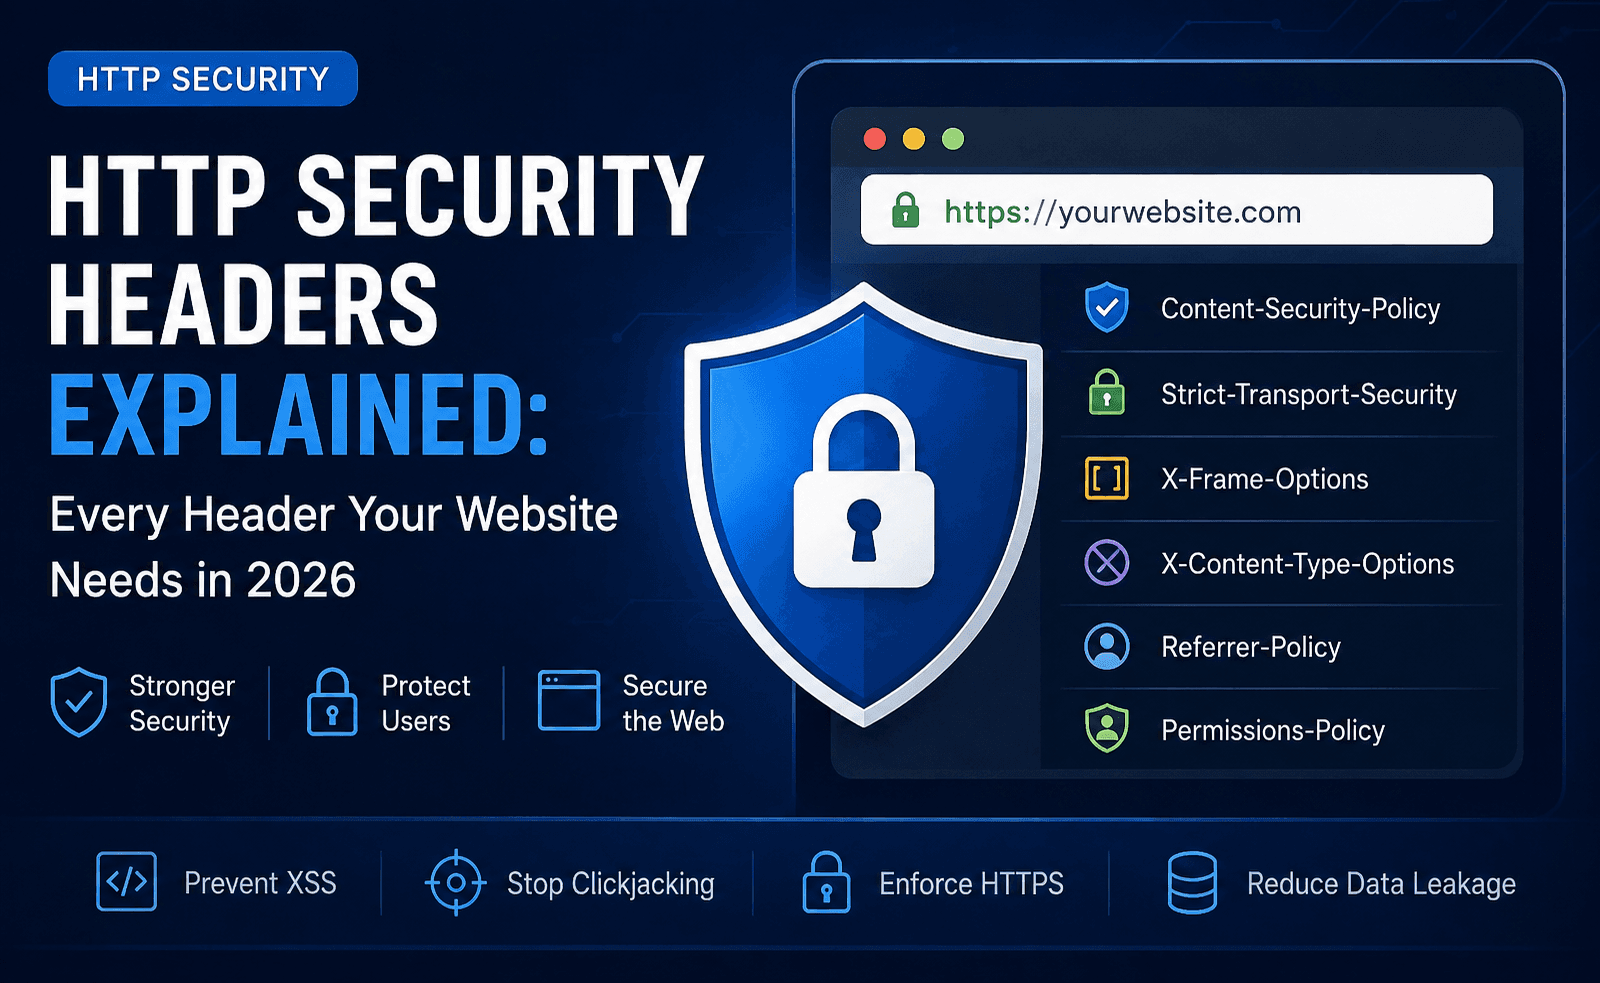
7. Missing Security Headers
What it is: HTTP security headers are free, one-line defenses against XSS, clickjacking, MIME sniffing, and information disclosure. Yet they're still missed in thousands of production sites.
Critical Headers Checklist:
| Header | Purpose |
|---|---|
Content-Security-Policy |
Prevent XSS, data injection |
Strict-Transport-Security |
Force HTTPS |
X-Frame-Options |
Prevent clickjacking |
X-Content-Type-Options |
Stop MIME sniffing |
Referrer-Policy |
Control referrer data leakage |
Permissions-Policy |
Restrict browser APIs (camera, mic) |
Fix:
add_header X-Frame-Options "DENY";
add_header X-Content-Type-Options "nosniff";
add_header Referrer-Policy "strict-origin-when-cross-origin";
add_header Strict-Transport-Security "max-age=31536000; includeSubDomains; preload";
💡 Test your headers at VAPT Insights — Security Headers Scanner
8. Overly Permissive CORS Policy
What it is: CORS (Cross-Origin Resource Sharing) is misconfigured to allow any origin (Access-Control-Allow-Origin: *), or worse, dynamically reflects the Origin header without validation — allowing any website to make authenticated requests on a user's behalf.
Dangerous Pattern:
// Blindly reflecting Origin header — NEVER do this
res.setHeader('Access-Control-Allow-Origin', req.headers.origin);
res.setHeader('Access-Control-Allow-Credentials', 'true');
Fix:
- Whitelist specific trusted origins.
- Never combine
Allow-Credentials: truewith wildcard origins. - Validate origins server-side against an allowlist.
9. Cookies Without Secure Flags
What it is: Session cookies missing Secure, HttpOnly, or SameSite attributes can be stolen via network interception, XSS, or CSRF attacks.
Vulnerable vs Secure:
# Vulnerable
Set-Cookie: session=abc123

# Secure
Set-Cookie: session=abc123; Secure; HttpOnly; SameSite=Strict; Path=/
Fix: Always set all three attributes on session and authentication cookies.
10. Insecure TLS/SSL Configuration
What it is: Servers supporting deprecated protocols (TLS 1.0, TLS 1.1, SSLv3), weak cipher suites (RC4, DES, EXPORT ciphers), or self-signed certificates in production.
Fix:
- Use TLS 1.2 minimum, TLS 1.3 preferred.
- Use Mozilla's SSL Configuration Generator.
- Test with
testssl.shor SSL Labs.
ssl_protocols TLSv1.2 TLSv1.3;
ssl_ciphers ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256;
ssl_prefer_server_ciphers off;
11. Open Cloud Storage Buckets (S3, GCS, Azure Blob)
What it is: Cloud storage buckets configured with public read (or worse, public write) access — unintentionally exposing user PII, internal documents, backups, and secrets.
Real-World Scale: In 2025, researchers discovered 2,300+ publicly accessible AWS S3 buckets containing PII data from healthcare and e-commerce sectors.
Fix:
- Use
aws s3api get-bucket-aclto audit all buckets. - Enable S3 Block Public Access at the account level.
- Use AWS Config rules to alert on public bucket creation.
- Enable access logging and monitor with CloudTrail.
12. Unprotected GraphQL Introspection in Production
What it is: GraphQL's introspection feature, enabled by default, allows anyone to query the entire schema — types, queries, mutations, fields — making it a roadmap for attackers.
Fix:
- Disable introspection in production environments.
- If needed for internal tools, restrict it to authenticated/internal users.
// Apollo Server
const server = new ApolloServer({
  introspection: process.env.NODE_ENV !== 'production',
});
13. Server Version Disclosure via HTTP Headers
What it is: Web servers leaking their name and version via Server, X-Powered-By, or X-AspNet-Version headers — helping attackers fingerprint and target known CVEs.
Server: Apache/2.4.51 (Ubuntu)
X-Powered-By: PHP/8.1.2
X-AspNet-Version: 4.0.30319
Fix:
server_tokens off;
ServerSignature Off
ServerTokens Prod
14. JWT Misconfigurations
What it is: JSON Web Token vulnerabilities caused by misconfiguration, including:
alg: noneattack (accepting unsigned tokens)- Using
HS256with a weak or publicly known secret - Not validating
exp,iss, oraudclaims - Storing JWTs in
localStorage(XSS accessible)
Fix:
- Use asymmetric algorithms (RS256, ES256) for distributed systems.
- Always validate all claims server-side.
- Store tokens in
HttpOnlycookies, not localStorage. - Rotate signing keys periodically.
15. Insecure Direct Object References (IDOR) via Predictable IDs
What it is: Using sequential or predictable IDs in URLs (/api/invoices/1234) without authorization checks, allowing attackers to access other users' resources by simply changing the ID.
Fix:
- Use UUIDs or opaque tokens instead of sequential integers.
- Always verify that the authenticated user is authorized to access the requested resource — even if the ID is valid.
🟡 MEDIUM
16. Missing Rate Limiting on Sensitive Endpoints
What it is: Login, password reset, OTP verification, and API endpoints without rate limiting are vulnerable to brute force, credential stuffing, and enumeration attacks.
Fix:
- Implement rate limiting per IP and per account.
- Use exponential backoff and account lockout.
- Add CAPTCHA after N failed attempts.
# Nginx rate limiting
limit_req_zone $binary_remote_addr zone=login:10m rate=5r/m;
limit_req zone=login burst=10 nodelay;
17. Misconfigured Content Security Policy (CSP)
What it is: A CSP that's too permissive defeats its own purpose. Common mistakes:
unsafe-inlineallows inline scripts (bypasses XSS protection)unsafe-evalallowseval()(dangerous)*as a source wildcard- Missing
default-srcdirective
Fix:
Build a strict CSP using nonces or hashes.
Content-Security-Policy: default-src 'self'; script-src 'self' 'nonce-{random}'; object-src 'none';
18. Lack of Subresource Integrity (SRI) for CDN Assets
What it is: Loading JavaScript or CSS from a CDN without SRI means if the CDN is compromised, attackers can inject malicious code into your site for all visitors.
Fix:
<script
  src="https://cdn.example.com/jquery.min.js"
  integrity="sha384-abc123..."
  crossorigin="anonymous">
</script>
19. Exposed Git Repository on Web Server
What it is: .git/ folder left accessible on the web root, allowing attackers to reconstruct the entire source code — including hardcoded secrets, credentials, and business logic.
Test:
https://example.com/.git/config
Fix:
- Block access to
.git/in your web server config. - Run automated scans using tools like
git-dumperin your VAPT process.
20. Missing Account Lockout / Brute Force Protection
What it is: No mechanism to slow down or stop repeated failed login attempts — making accounts vulnerable to credential stuffing and dictionary attacks.
Fix:
- Lock accounts after N failed attempts (with notification to user).
- Use CAPTCHA and progressive delays.
- Monitor and alert on unusual login patterns.
21. Insecure Password Reset Flow
What it is: Password reset implementations with flaws such as:
- Predictable or short reset tokens
- Tokens that never expire
- Token reuse after use
- Reset links sent over HTTP
- Username/email enumeration via different responses
Fix:
- Use cryptographically random tokens (≥ 256 bits).
- Expire tokens after 15–30 minutes and after first use.
- Return identical responses for valid/invalid emails.
22. Missing robots.txt Awareness + Admin Path Exposure
What it is: robots.txt intended to hide paths from search engines, but unintentionally listing sensitive paths (/admin, /backup, /internal) — which attackers actively harvest.
Fix:
- Don't rely on
robots.txtfor security — it's a public file. - Use proper authentication and authorization on all sensitive routes.
- Avoid listing sensitive paths in
robots.txt.
23. Misconfigured Reverse Proxy (Nginx/Cloudflare/AWS ALB)
What it is: Reverse proxy misconfigurations that allow:
- Request smuggling (inconsistent header parsing between proxy and origin)
- Path traversal bypasses (
/admin→/admin/../private) - Origin server IP exposure (bypassing WAF/DDoS protection)
- Cache poisoning via unvalidated headers
Fix:
- Keep proxy and origin server versions synchronized.
- Use consistent request parsing settings.
- Never expose origin server IPs publicly.
- Test with tools like
smuggleror Burp Suite's HTTP/2 scanner.
24. Insufficient Logging and Monitoring
What it is: Applications that don't log security events — failed logins, privilege escalations, input validation failures — leaving organizations blind to active attacks.
What to Log:
- Authentication events (success and failure)
- Access control failures
- Input validation errors
- All admin actions
- Unusual data access patterns
Fix:
- Implement centralized logging (ELK Stack, Datadog, Splunk).
- Set up real-time alerts for anomalous patterns.
- Ensure logs are tamper-proof and stored off the application server.
25. AI/LLM API Endpoint Misconfiguration (2026 Emerging)
What it is: As AI features become standard, new misconfiguration patterns have emerged:
- Exposed system prompts via
/api/chat/configor verbose error responses - Missing rate limits on AI inference endpoints (leading to financial abuse)
- Over-privileged AI agent permissions allowing unintended file system or API access
- Prompt injection via unsanitized user input passed directly to LLM APIs
- Leaked API keys for OpenAI, Anthropic, or Gemini in client-side JavaScript
Real-World (2025–2026): Multiple startups faced four- and five-figure OpenAI bills after attackers discovered unprotected /api/generate endpoints and used them as free AI services.
Fix:
- Rate-limit all AI endpoints aggressively.
- Never expose AI API keys in frontend code.
- Treat AI inputs as untrusted; sanitize and validate before passing to LLMs.
- Implement budget alerts on all AI API accounts.
- Keep system prompts server-side only.
Summary Table
| # | Misconfiguration | Severity | OWASP Category |
|---|---|---|---|
| 1 | Default Credentials | 🔴 Critical | A05 – Misconfiguration |
| 2 | Exposed .env Files |
🔴 Critical | A02 – Cryptographic Failures |
| 3 | Directory Listing | 🔴 Critical | A05 – Misconfiguration |
| 4 | Verbose Error Messages | 🔴 Critical | A05 – Misconfiguration |
| 5 | Unauth Admin Endpoints | 🔴 Critical | A01 – Broken Access Control |
| 6 | Spring Actuator Exposed | 🔴 Critical | A05 – Misconfiguration |
| 7 | Missing Security Headers | 🟠 High | A05 – Misconfiguration |
| 8 | Permissive CORS | 🟠 High | A05 – Misconfiguration |
| 9 | Insecure Cookies | 🟠 High | A02 – Cryptographic Failures |
| 10 | Weak TLS/SSL | 🟠 High | A02 – Cryptographic Failures |
| 11 | Open Cloud Buckets | 🟠 High | A05 – Misconfiguration |
| 12 | GraphQL Introspection | 🟠 High | A05 – Misconfiguration |
| 13 | Server Version Disclosure | 🟠 High | A05 – Misconfiguration |
| 14 | JWT Misconfig | 🟠 High | A02 – Cryptographic Failures |
| 15 | IDOR | 🟠 High | A01 – Broken Access Control |
| 16 | Missing Rate Limiting | 🟡 Medium | A07 – Auth Failures |
| 17 | Weak CSP | 🟡 Medium | A05 – Misconfiguration |
| 18 | Missing SRI | 🟡 Medium | A08 – Software Integrity |
| 19 | Exposed Git Repo | 🟡 Medium | A05 – Misconfiguration |
| 20 | No Account Lockout | 🟡 Medium | A07 – Auth Failures |
| 21 | Insecure Password Reset | 🟡 Medium | A07 – Auth Failures |
| 22 | robots.txt Exposure | 🟡 Medium | A05 – Misconfiguration |
| 23 | Reverse Proxy Misconfig | 🟡 Medium | A05 – Misconfiguration |
| 24 | Insufficient Logging | 🟡 Medium | A09 – Logging Failures |
| 25 | AI/LLM API Misconfiguration | 🟠 High | A05 – Misconfiguration (Emerging) |
How to Find These in Your Own Applications
Scan Your Website with VAPT Insights
Stop guessing. VAPT Insights automatically checks your website for these misconfigurations — for free.
- 🔍 Security Headers Scanner — Instantly detect missing or misconfigured HTTP security headers at vaptinsights.com/security-headers
- 🔐 Certificate Analysis — Audit your SSL/TLS certificates for expiry, weak algorithms, and chain issues at vaptinsights.com/certificate-analysis
- 📦 Deep SBOM Inventory Tracking & Risk Auditing — Track every dependency in your software supply chain and identify vulnerabilities before they're exploited at vaptinsights.com
- 🛡️ Continuous Monitoring — Get alerted the moment a misconfiguration appears on your site
- 📊 Detailed Reports — Actionable insights with severity ratings and fix recommendations
- ✅ Zero Setup — No installation needed, just enter your URL and scan
Manual Testing Checklist
- Check all response headers with browser dev tools or curl
- Test common sensitive paths (
/.git,/.env,/actuator,/admin) - Verify cookie flags in the browser's Application tab
- Check TLS rating at SSL Labs
- Test CORS with a curl request including
Origin: https://evil.com - Review cloud bucket permissions via provider console
Final Thoughts
Security misconfigurations are not a sign of negligent developers — they're a sign of complex systems without automated guardrails. The best defense in 2026 is:
- Shift Left: Integrate security checks into CI/CD pipelines, not just pre-release testing.
- Automate: Use IaC security scanners (Checkov, tfsec) to catch misconfigs before deployment.
- Monitor Continuously: Misconfigurations can be introduced by updates, new team members, or dependency upgrades.
- Red Team Regularly: Manual VAPT engagements catch what automated tools miss.
The best security posture isn't about being unhackable — it's about reducing your attack surface until attackers move on to an easier target.
Learn More
Want to check whether your website has any of these misconfigurations?
Run a free scan with VAPT Insights to identify missing or misconfigured security headers and discover practical recommendations to improve your website's security posture.
You can also explore more security guides, compliance resources, and best practices on the VAPT Insights blog.