Product Showcase
Sleek Security Control Center
Take a tour of VAPTInsights premium application security suite. Built with high-fidelity telemetry, interactive trees, and actionable vulnerability trackers.
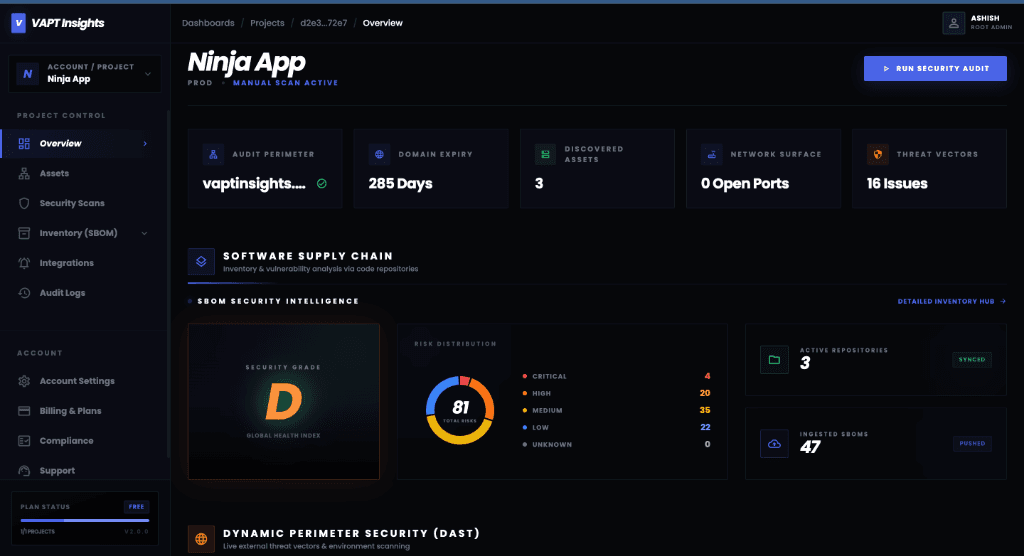
Interactive Exposure Overview
Get an aggregate view of critical vulnerabilities, network exposure trend analysis, and live asset defense state from a single high-fidelity dashboard.
Simple Integration Workflow
Securing Your Supply Chain in Three Steps
Continuous automation from repository upload to live remediation.
Connect Repo / Upload SBOM
Integrate your codebase via GitHub/GitLab, trigger hooks on new commits, or drag & drop raw CycloneDX / SPDX files directly.
Scan Dependencies & Security
Our engine discovers nested vulnerabilities, checks SSL headers, maps supply chain risks, and flags CVE anomalies automatically.
> Parsing application dependency matrix...
> Found package: openssl-node (v1.2.0) [CVE-2024-XXXX]
> WARNING: High-Severity vulnerability detected in deep transitive node!
> Generating complete software bill of materials...
Deep SBOM Inventory Tracking & Risk Auditing
Protect your operations from zero-day downstream exploits. VAPTInsights automatically parses **CycloneDX** and **SPDX** standard catalogs, indexes nested dependencies, monitors software inventory health, and guarantees supply chain compliance mapping against NIST and ISO 27001 requirements.
Robust Dev Ecosystem
Seamless Integrations
Connect your existing toolchain and alert pipelines immediately.
Core Differentiation
Why Modern Teams Choose VAPTInsights
We build defense systems that engineers actually enjoy using.
Lightweight Setup
No complex agents, servers, or invasive software configurations needed. Plugs in via secure webhooks and web perimeter scans.
Lightspeed Audits
Distributed serverless edge architecture ensures hundreds of endpoints and dependency modules are scanned in seconds.
Interactive Scanning Directory
Security Scanners
Try our lightweight sandboxed scanning modules immediately.
Headers Scanner
Audits HTTP security response headers like CSP, HSTS, X-Content-Type, and CORS controls.
SSL/TLS Analyzer
Checks handshake validity, cipher suites, TLS version support, and certificate chain expiry.
DPDP Technical Readiness
Evaluate website technical safeguards, cookie consent, and public notices for DPDP compliance.
Enterprise Trust Signals
Privacy-First Security
We secure your digital envelope without compromising operational data integrity.
Privacy-First Setup
No read permissions to your private source code. We scan compiled package metadata and peripheral targets safely.
Full Envelope Encryption
Data in transit uses TLS 1.3 and database storage uses isolated AES-256 keys to secure all customer configuration files.
Responsible Disclosure
Pricing Plans
Scale Your Security.
Simple, transparent pricing for teams of all sizes.
Early Stage
Free
- 1 Project
- 1 Main Asset
- 1 Manual Scan / Month
- Basic PDF Reports
- Community Email Support
- Limited Severity Visibility
- 0 Subdomains
Growing Business
Pro
- Includes All Free Features
- 2 Projects
- 3 Subdomains per Project
- Weekly Automated Scans
- Slack & Email Alerts
- Full Vulnerability Details
- Risk Scoring Dashboard
- Branded PDF Reports
- Compliance (DPDP + OWASP)
Business Scale
Growth
- Includes All Pro Features
- 20 Assets
- Daily Scans
- API & Authenticated Scans
- GitHub @ CI/CD Access
- Role-based Access
- Priority Support
- Compliance Summary Export
Enterprise Grade
Enterprise
- Includes All Growth Features
- Unlimited Assets
- Dedicated Account Manager
- Custom Compliance Mapping
- Executive-level Reporting
- SLA Guarantee
- On-prem Deployment Option
- Dedicated Analyst