Why SecurityHeaders.com is Not Enough for Continuous Perimeter Protection
If you have ever audited your web application's HTTP response headers, you have probably used SecurityHeaders.com. It's a fantastic, free tool that gives you a quick letter grade (from A+ to F) by inspecting headers like Content-Security-Policy (CSP), Strict-Transport-Security (HSTS), and X-Frame-Options.
But while a one-off scan is perfect for a quick sanity check, it creates a false sense of security for production systems.
Here is why static, on-demand scanners fail to protect modern systems, and why your organization needs Continuous Automated Perimeter Protection.
1. Zero Visibility on Configuration Drift
Websites are not static. Marketing teams deploy tags, DevOps updates load balancers, CDN rules are modified, and microservices are redeployed multiple times a day.
- The Static Scanner Gap: If a CDN update accidentally strips your
Content-Security-Policyheader at 2 AM, SecurityHeaders.com won't know. You are left completely exposed to Cross-Site Scripting (XSS) and clickjacking until you manually run another scan. - The Continuous VAPT Solution: VAPT Insights runs automated, scheduled sweeps (daily or weekly) across all your verified domains and subdomains, immediately catching and alerting you to any sudden configuration drifts.
2. The Danger of Silent SSL Certificate Expirations
A header scanner only reads headers. It does not analyze the underlying cryptographic health of your server. Your headers might look flawless, but if your SSL/TLS certificate expires, or if your server allows weak, outdated cipher suites (like TLS 1.0 or 1.1), attackers can intercept customer traffic via Man-in-the-Middle (MITM) attacks.
Continuous perimeter security monitors your SSL expiry thresholds, tracking remaining certificate days, validity records, and security cipher configurations, warning you well before browsers flag your site as "Not Secure."
3. No Subdomain Discovery & Asset Mapping
Large platforms are composed of multiple subdomains (e.g., api.yoursite.com, admin.yoursite.com, staging.yoursite.com).
- The Manual Scanner Gap: Static checkers require you to know and input every single URL manually. You cannot protect assets you don't know exist. Forgotten, orphaned staging sites are an attacker's absolute favorite entry point.
- The Intelligent Discovery Solution: VAPT Insights executes automated subdomain enumeration and port scanning, mapping out your entire active digital perimeter and identifying insecure entry points across your entire asset footprint.
🌟 Elevate Your Protection with VAPT Insights
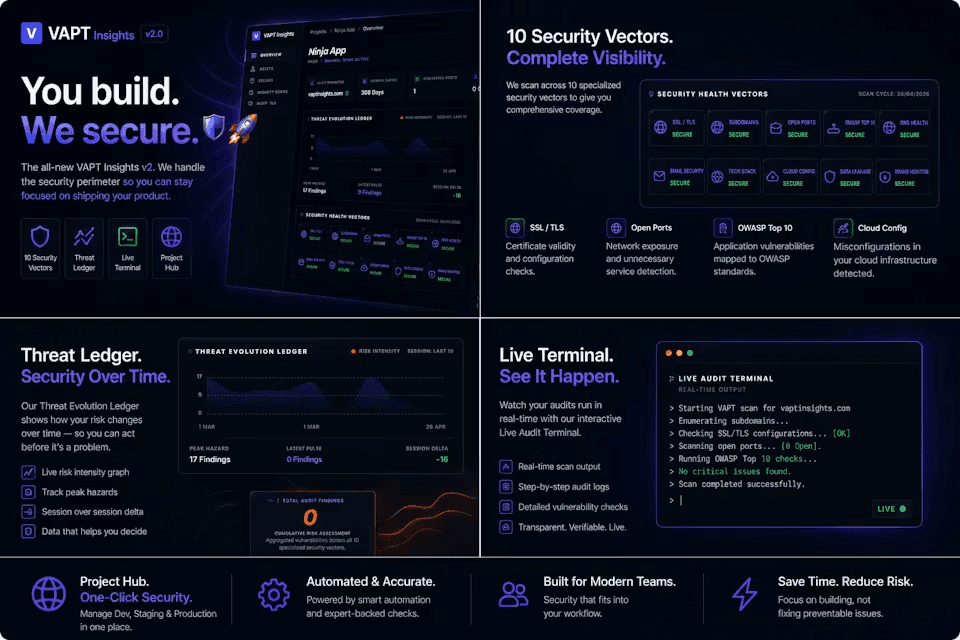
VAPT Insights goes beyond the letter grade to deliver enterprise-grade automated protection:
- Webhook & Slack Pipelines: Connect alerts directly into your Slack, Discord, or MS Teams rooms. Get notified the second a header changes.
- Branded executive-level PDF Reports: Export beautifully formatted, audit-ready PDF reports with precise code-level remediation steps.
- OWASP Compliance Alignment: Automatically maps scanner results to leading global frameworks like DPDP 2023, OWASP, GDPR, and PCI-DSS.
Stop auditing retrospectively. Start monitoring proactively.