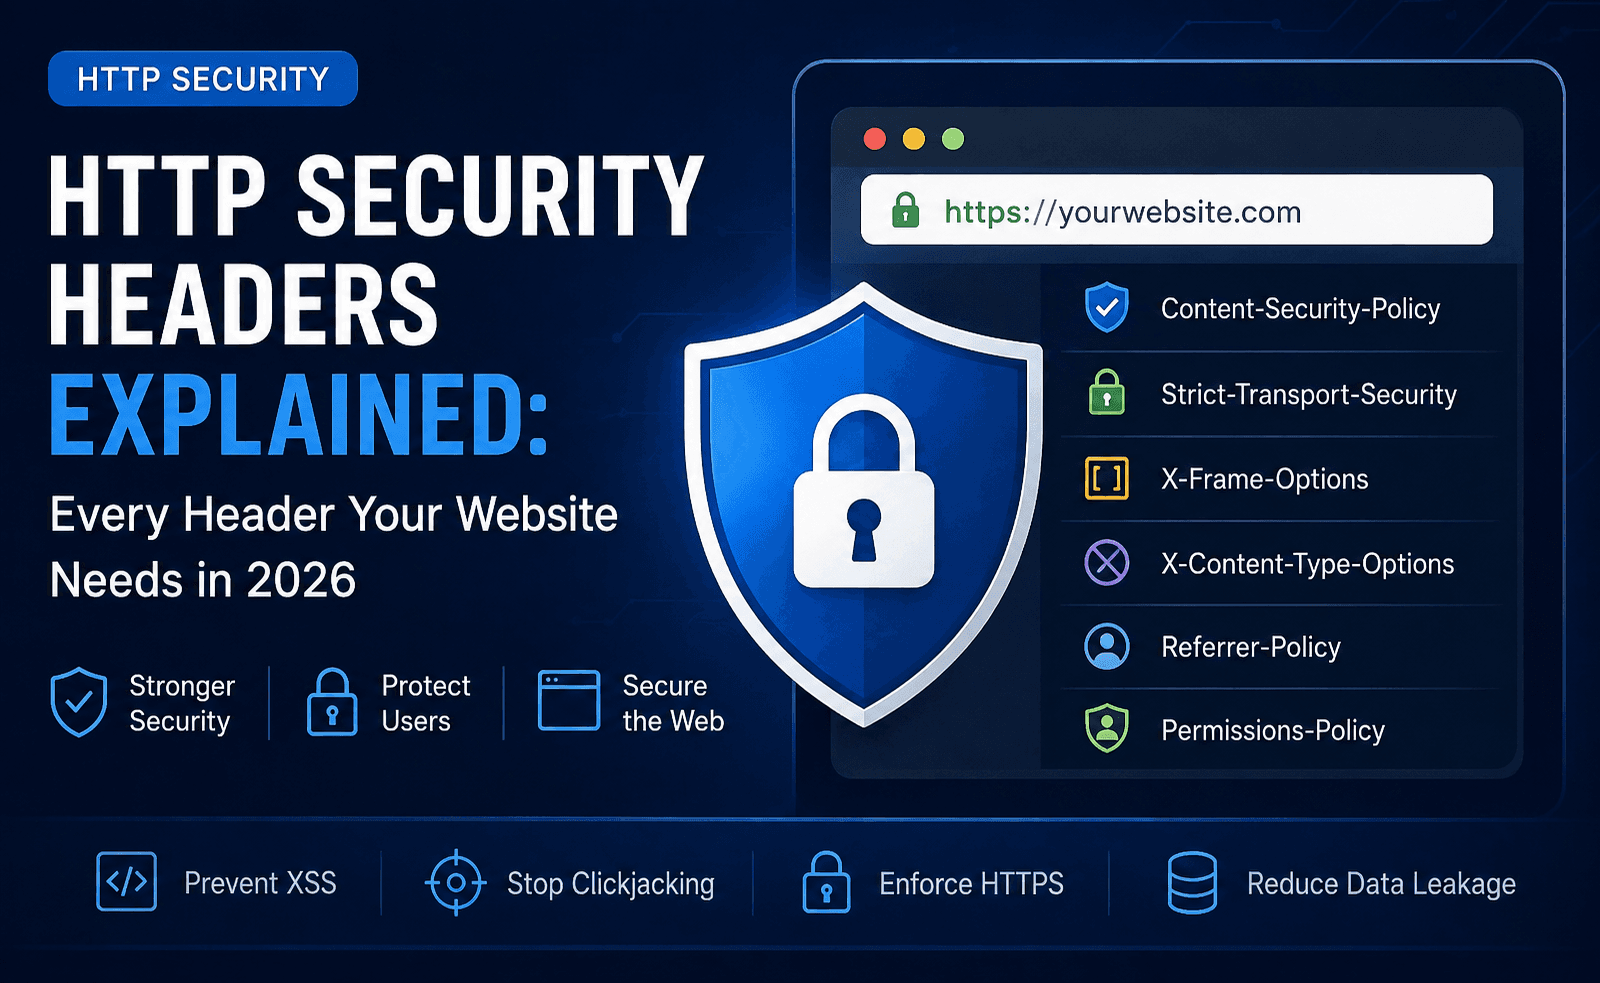
HTTP Security Headers Explained: Every Header Your Website Needs in 2026
When someone visits your website, their browser doesn't just download HTML, CSS, and JavaScript. Every response from your server also includes HTTP response headers—small pieces of information that tell the browser how to behave.
Some of these headers play a critical role in security.
They help protect your website against attacks like Cross-Site Scripting (XSS), clickjacking, MIME-type sniffing, insecure connections, and accidental data leakage.
Despite being one of the simplest security improvements, missing or misconfigured HTTP security headers remain a common issue across websites of all sizes.
In this guide, you'll learn what HTTP security headers are, why they matter, which ones you should use, and how to verify your website's configuration.
What Are HTTP Security Headers?
HTTP security headers are response headers sent by your web server that instruct browsers to enforce specific security policies.
Unlike firewalls or antivirus software, these headers work directly inside the user's browser, adding an extra layer of protection.
For example, a browser can be instructed to:
- Only communicate over HTTPS
- Prevent loading malicious scripts
- Stop other websites from embedding your pages
- Disable MIME type sniffing
- Limit what information is shared with external websites
A few configuration changes can significantly improve your application's security posture.
Why Are They Important?
Without proper security headers, your application may become vulnerable to attacks that are otherwise easy to prevent.
Security headers help defend against:
- Cross-Site Scripting (XSS)
- Clickjacking
- Man-in-the-Middle attacks
- MIME-type confusion
- Information leakage
- Unsafe browser behavior
They also demonstrate adherence to security best practices and are commonly reviewed during security assessments and penetration tests.
Essential HTTP Security Headers
1. Content-Security-Policy (CSP)
The Content Security Policy header controls which resources your website is allowed to load.
It is one of the most effective defenses against Cross-Site Scripting (XSS).
Example
Content-Security-Policy: default-src 'self';
A well-designed CSP reduces the impact of injected malicious JavaScript.
2. Strict-Transport-Security (HSTS)
HSTS tells browsers to always use HTTPS when connecting to your website.
Example
Strict-Transport-Security: max-age=31536000; includeSubDomains; preload
Benefits include:
- Prevents protocol downgrade attacks
- Protects users on public Wi-Fi
- Enforces encrypted communication
3. X-Frame-Options
This header prevents your website from being embedded inside an iframe on another website.
Example
X-Frame-Options: DENY
It protects users against clickjacking attacks.
4. X-Content-Type-Options
Browsers sometimes try to guess the content type of files.
This behavior can introduce security risks.
Use:
X-Content-Type-Options: nosniff
to disable MIME-type sniffing.
5. Referrer-Policy
Controls how much referrer information is shared with other websites.
Example:
Referrer-Policy: strict-origin-when-cross-origin
This helps reduce accidental exposure of sensitive URLs.
6. Permissions-Policy
Permissions-Policy allows you to control access to browser features.
Example:
Permissions-Policy: camera=(), microphone=(), geolocation=()
Disable features your application does not need.
7. Cross-Origin Security Headers
Modern browsers support additional headers that strengthen isolation between websites.
These include:
- Cross-Origin-Opener-Policy
- Cross-Origin-Embedder-Policy
- Cross-Origin-Resource-Policy
These headers are increasingly important for modern web applications and advanced browser security.
Common Mistakes
Many websites make one or more of these mistakes:
- Missing Content Security Policy
- No HSTS header
- Using outdated X-XSS-Protection configurations
- Weak Referrer Policy
- Allowing pages to be framed
- Forgetting security headers on API responses
- Different headers across environments
Regular security reviews help identify and fix these issues.
How to Check Your Website
You can inspect response headers manually using your browser's developer tools or command-line utilities.
For ongoing security, it's useful to automate these checks as part of your deployment or security review process.
A dedicated security header scanner can quickly identify missing or misconfigured headers and provide guidance on improving your setup.
Best Practices
- Always serve your website over HTTPS.
- Deploy a carefully tested Content Security Policy.
- Enable HSTS after confirming HTTPS is correctly configured.
- Apply consistent security headers across all pages and APIs.
- Review your configuration after infrastructure or application changes.
- Include security header validation in regular security assessments.
Final Thoughts
HTTP security headers are a simple yet powerful way to strengthen your website's defenses. They require minimal implementation effort but can significantly reduce the risk of common web attacks when configured correctly.
Whether you're building a small business website, an enterprise application, or a public API, reviewing and maintaining your security headers should be part of your standard security checklist.
Small improvements in configuration today can help prevent larger security issues tomorrow.
Learn More
Want to check whether your website is using the right HTTP security headers?
Run a free scan with VAPT Insights to identify missing or misconfigured security headers and discover practical recommendations to improve your website's security posture.
You can also explore more security guides, compliance resources, and best practices on the VAPT Insights blog.