Continuous SBOM Monitoring with Trivy and VAPTInsights
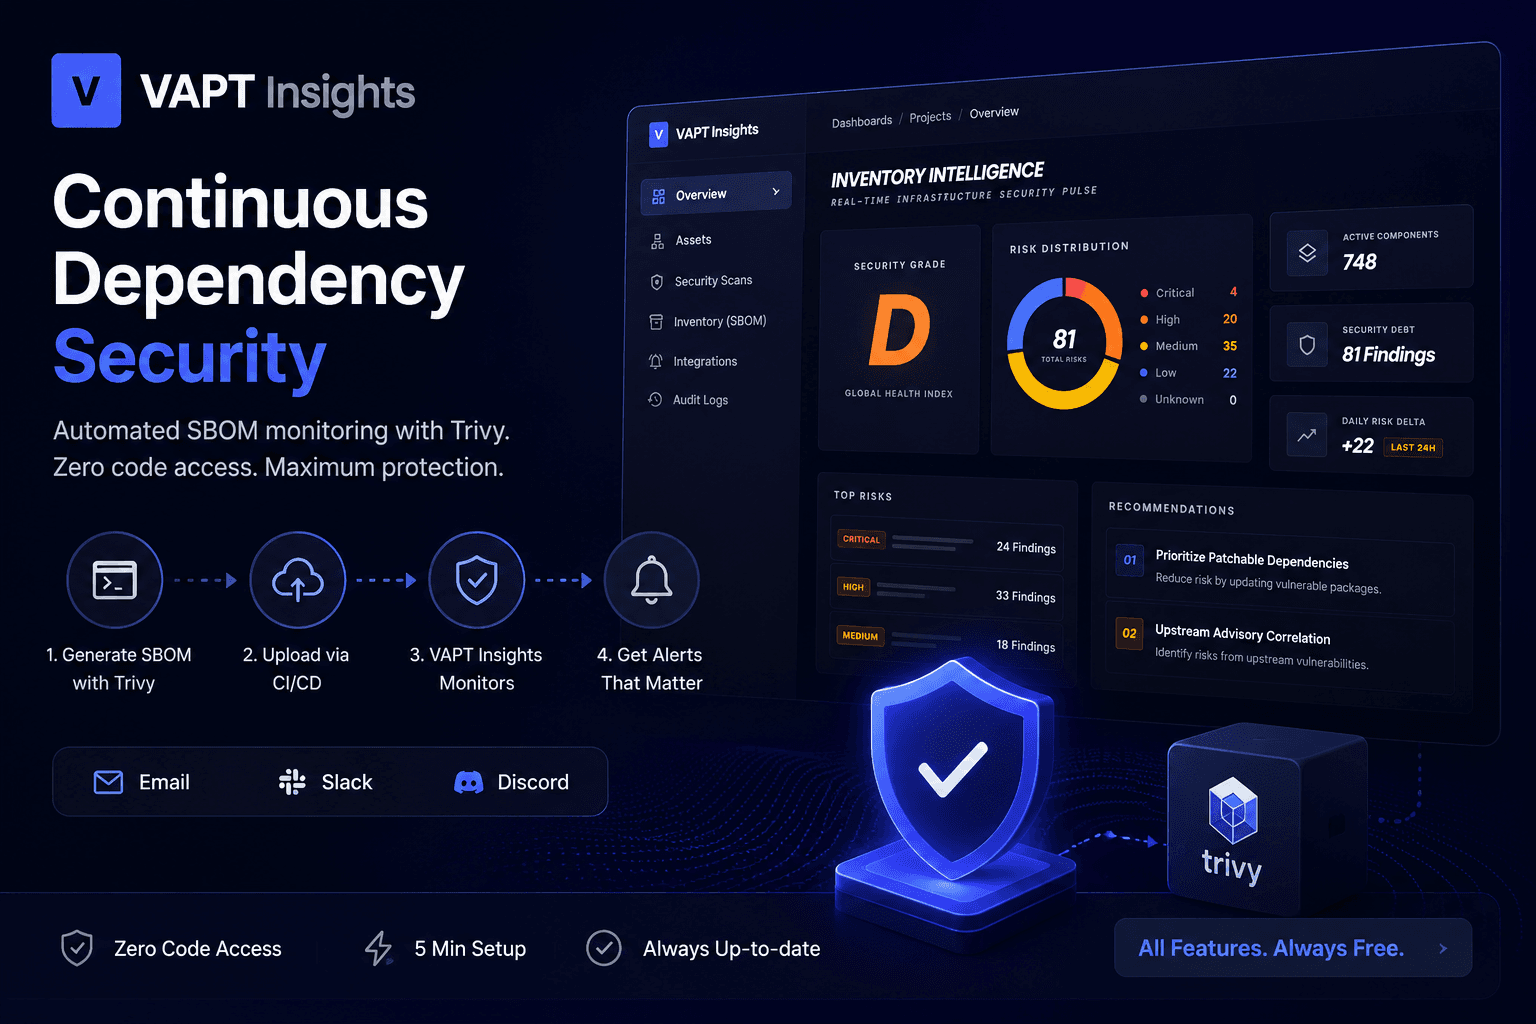
Secure Your Software Supply Chain with SBOM Integration using Trivy
Modern applications rely heavily on open-source packages, third-party libraries, and transitive dependencies. Every day, new vulnerabilities are disclosed in packages that development teams use directly or indirectly.
The biggest problem is not just identifying vulnerabilities during development — it is continuously monitoring deployed applications after release.
A dependency that appears secure today may become critical tomorrow because of a newly published CVE.
This is exactly why SBOM (Software Bill of Materials) monitoring is becoming an essential part of modern software security.
At VAPTInsights, we help teams continuously monitor dependencies using automated SBOM integration powered by CI/CD pipelines and Trivy.
What is an SBOM?
SBOM stands for Software Bill of Materials.
It is a structured inventory of all software components, dependencies, libraries, and packages used inside an application.
You can think of it as an ingredient list for your software.
An SBOM typically contains:
- Direct dependencies
- Transitive (indirect) dependencies
- Package versions
- Component metadata
- License information
- Dependency relationships
For example, your application may directly install Express.js, React, or NestJS, but those packages internally depend on hundreds of additional libraries.
Many vulnerabilities are discovered inside these indirect dependencies.
Without an SBOM, teams often do not even know vulnerable packages exist in production systems.
SBOMs provide visibility into:
- What is running in your application
- Which packages are vulnerable
- Which versions are deployed
- Which dependencies require updates
This visibility is critical for modern software supply chain security.
Why SBOM Monitoring Matters
Software supply chain attacks are increasing rapidly.
Attackers now frequently target:
- Open-source ecosystems
- Package registries
- Transitive dependencies
- CI/CD pipelines
- Outdated production dependencies
Traditional vulnerability scanning is no longer enough because:
- Scans are often one-time
- Reports become outdated quickly
- Newly published CVEs appear daily
- Deployed applications remain unmonitored
A package that was secure during deployment may become vulnerable weeks later.
This is where continuous SBOM monitoring becomes important.
SBOM monitoring helps organizations:
- Continuously track dependency risks
- Monitor newly disclosed CVEs
- Detect vulnerable transitive dependencies
- Improve software supply chain visibility
- Reduce exposure to dependency-based attacks
- Improve compliance readiness
- Maintain visibility into production deployments
Continuous SBOM Monitoring with VAPTInsights
At VAPTInsights, we simplify SBOM-based dependency tracking without requiring direct access to your codebase.
Our platform continuously monitors uploaded SBOMs and automatically checks them against newly disclosed vulnerabilities.
You can:
- Add unlimited repositories
- Upload SBOMs automatically through CI/CD
- Track dependencies continuously
- Monitor production deployments
- Receive vulnerability alerts
- Manage multiple projects from one dashboard
The complete setup takes less than 5 minutes.
Everything Included in the Free Version
We believe software supply chain security should be accessible to all developers and teams.
That’s why all core SBOM monitoring features are available in the free version.
Free users can:
- Add unlimited repositories
- Upload SBOMs through CI/CD
- Continuously monitor dependencies
- Track transitive vulnerabilities
- Receive critical vulnerability alerts
- Configure email notifications
- Add Slack webhook integrations
- Add Discord webhook integrations
- Access centralized dependency tracking
No complicated enterprise-only restrictions for basic dependency security monitoring.
Zero Code Access Required
Most dependency monitoring platforms require:
- Repository access
- GitHub app installation
- Source code permissions
- Repository cloning
- Additional agents
VAPTInsights works differently.
We never access your source code.
You only generate an SBOM file inside your CI/CD workflow and upload it securely to VAPTInsights.
Your code always stays inside your infrastructure.
This provides:
- Better privacy
- Easier enterprise adoption
- Reduced compliance concerns
- Faster integration
- Safer third-party security monitoring
No repository cloning. No invasive agents. No source code exposure.
Why We Use Trivy for SBOM Generation
We currently recommend using Trivy for SBOM generation because it is:
- Widely adopted
- Open source
- Fast and lightweight
- CI/CD friendly
- Easy to automate
- Trusted by DevOps and security teams
- Supports industry-standard SBOM formats
Example Trivy command:
trivy fs --format cyclonedx --output sbom.json .
This generates a CycloneDX SBOM file that can be uploaded directly to VAPTInsights.
Support for additional SBOM tools and formats will be added in future releases.
Simple CI/CD Integration
The integration workflow is intentionally simple.
Step 1 — Generate SBOM using Trivy
Generate the SBOM inside your CI/CD pipeline:
trivy fs --format cyclonedx --output sbom.json .
Step 2 — Create API Access Token
Create an API Access Token from your VAPTInsights dashboard.
Step 3 — Upload SBOM
Upload the generated SBOM using our API/Webhook integration.
Step 4 — Continuous Monitoring Starts
Once uploaded, VAPTInsights continuously monitors the SBOM against newly disclosed vulnerabilities and CVEs.
We recommend uploading SBOMs from:
- UAT environments
- Staging environments
- Production deployments
This provides accurate dependency visibility for deployed applications.
Supported CI/CD platforms include:
- GitHub Actions
- GitLab CI
- Jenkins
- Azure DevOps
- Bitbucket Pipelines
- Custom CI/CD systems
Official CI/CD integration guide:
VAPTInsights Pipeline Integration Documentation
Smart Vulnerability Monitoring
Once your SBOM is uploaded, VAPTInsights continuously checks your dependencies against:
- Newly disclosed CVEs
- Dependency vulnerability databases
- Security advisories
- Critical package disclosures
You receive:
- Daily security summaries
- Weekly vulnerability reports
- Critical vulnerability alerts
We focus on actionable notifications — not spam.
Alerts are sent only when newly disclosed vulnerabilities affect your tracked dependencies.
This helps teams focus on real security risks instead of excessive noise.
Notification Integrations
VAPTInsights supports multiple notification channels for security and development teams.
Email Notifications
- Add up to 5 recipients
- Receive daily and weekly reports
- Get critical alerts instantly
Slack Integration
- Real-time webhook-based alerts
- Easy integration with existing Slack channels
Discord Integration
- Lightweight webhook integration
- Instant vulnerability notifications
More integrations will be added in future releases.
What Makes VAPTInsights Different?
Many dependency scanning platforms only provide one-time scans or static reports.
They often require:
- Complex infrastructure
- Repository access
- Ongoing maintenance
- Manual scaling
- Large operational overhead
VAPTInsights focuses on continuous SBOM intelligence with minimal setup.
Continuous Monitoring Instead of One-Time Scans
Traditional scanners:
- Scan once
- Generate a report
- Stop monitoring
VAPTInsights:
- Continuously monitors uploaded SBOMs
- Detects newly disclosed vulnerabilities
- Tracks dependency risk over time
- Protects even inactive applications
This is critical because vulnerabilities are discovered daily.
No Infrastructure Maintenance
Some organizations deploy platforms like Dependency-Track directly.
While powerful, self-hosting requires:
- Infrastructure setup
- Database configuration
- Updates and patching
- Backup management
- Scaling infrastructure
- Monitoring uptime
- Notification management
- Operational maintenance
With VAPTInsights, we handle everything for you.
You focus on development while we manage:
- Dependency tracking infrastructure
- SBOM processing
- Vulnerability monitoring
- Alerting systems
- Platform maintenance
- Scaling and uptime
No operational burden. No maintenance overhead.
Just upload your SBOMs and start monitoring immediately.
Built for Modern DevOps Teams
VAPTInsights is designed for fast-moving engineering teams.
The platform integrates easily into existing development workflows without slowing teams down.
No complicated onboarding. No heavy setup. No source code access. No complex infrastructure management.
Just lightweight CI/CD integration and continuous monitoring.
Smart Alerts Without Spam
Security teams already receive too many alerts.
VAPTInsights focuses on:
- Relevant notifications
- Critical vulnerabilities
- Actionable reports
- Meaningful security insights
We prioritize signal over noise.
Built for Modern Software Supply Chain Security
SBOM adoption is rapidly becoming a core requirement for:
- Application security
- Software transparency
- Compliance readiness
- Vendor risk management
- Supply chain security
Organizations increasingly need:
- Dependency visibility
- Continuous monitoring
- Vulnerability traceability
- Production dependency intelligence
VAPTInsights helps teams adopt SBOM security quickly with:
- Minimal setup
- Zero code exposure
- CI/CD automation
- Continuous dependency intelligence
Final Thoughts
Software supply chain vulnerabilities evolve every day.
A package that appears safe today may become a critical production risk tomorrow.
Continuous SBOM monitoring is no longer optional for modern applications.
With VAPTInsights, you can:
- Continuously monitor dependency vulnerabilities
- Track transitive packages
- Secure unlimited repositories
- Receive actionable alerts
- Protect deployed applications
- Improve software supply chain visibility
All without exposing your source code or managing additional infrastructure.
Set up your SBOM integration in minutes and secure your software supply chain with automated dependency monitoring.